Bridging the Gap: Spanning Tree Protocol and EtherChannel

· 7 min read
Dario Cruz
Maintainer of DarioCruz.dev

Spanning Tree Blocking vs EtherChannel Bundling

Spanning Tree Protocol (STP) is the ultimate safety net for any Layer 2 network, but it comes with a frustrating catch: to prevent broadcast storms, it ruthlessly blocks redundant links. If you run four 1Gbps cables between two core switches, STP will shut down three of them, leaving you with 3Gbps of dark, wasted fiber. This is where EtherChannel steps in. By bundling physical links into a single logical connection, we can finally stop wasting bandwidth while keeping STP completely happy.

Mastering Spanning Tree Protocol (STP): From Amazon Warehouses to CCNA 200-301 Excellence

· 14 min read
Dario Cruz
Maintainer of DarioCruz.dev

Extended System ID Diagram

Hello all! Anyone who has watched a single misplaced patch cable trigger a massive broadcast storm—freezing CLI sessions and instantly taking down an entire floor—understands exactly why Layer 2 loops demand such terrifying respect.

Back when I worked as a IT Support Associate at Amazon, I was assigned to a project called Operation Carbon Shield. Our goal was to add Layer 3 switches directly into the IDF (Intermediate Distribution Frame) cabinets across the warehouse. Why? Because in a massive fulfillment center, all it takes is one well-meaning team member plugging an Ethernet cable into two active wall ports—or connecting a rogue unmanaged switch—to create a catastrophic Layer 2 loop. By pushing Layer 3 boundaries down to the IDF level, we drastically minimized the blast radius of any accidental loops created on the warehouse floor.

VLANs in Depth - Access Ports, Trunks, and Native VLANs Explained

· 11 min read
Dario Cruz
Maintainer of DarioCruz.dev

VLAN Architecture Overview

Hello all,

It's time to dive back into network architecture fundamentals! Between balancing work tasks and setting up lab scenarios in Packet Tracer, I've been spending a ton of time working through the Cisco CCNA 200-301 domains. As I study and lab out these concepts, I want to document what I'm learning, breaking down core networking concepts into practical, hands-on guides.

Let's kick things off with one of the absolute bedrock building blocks of enterprise switching: Virtual Local Area Networks (VLANs).

Mastering VLANs is easily one of the most critical milestones for anyone studying for the CCNA or managing campus networks. It isn't just about memorizing CLI command syntax; it's about deeply understanding how Ethernet frames are tagged, how switches handle traffic across trunk links, and how to write clean configuration lines that prevent network loops and security vulnerabilities.

Demystifying Subnetting - From Binary Math to Real-World Cisco IOS Configs

· 14 min read
Dario Cruz
Maintainer of DarioCruz.dev

IPv4 Subnetting & Addressing Architecture

Hello all,

It's been a busy couple of weeks balancing work, lab sessions, and CCNA prep. Lately, I've been spending a ton of time diving deep into Layer 3 network architecture—specifically, IP addressing and subnetting.

Subnetting is easily one of those topics that strikes fear into the hearts of anyone starting out in networking. When I first looked at CIDR notation and binary masks, it felt like trying to decipher matrix code. But once you break down why we divide networks and learn a few clever shortcuts, the lightbulb turns on, and it becomes second nature.

In this post, I want to take you through everything you need to master IPv4 addressing and subnetting—from the core theory and speed-calculation shortcuts to real-world Cisco IOS CLI configurations and troubleshooting gotchas.

Exposing Services using Cloudflare Tunnels

· 6 min read
Dario Cruz
Maintainer of DarioCruz.dev

Title card for the blog post: Exposing Services using Cloudflare Tunnels

Hello all,

It's been a while since my last post. Work and life have eaten up a good chunk of my time recently, but luckily I now have some breathing room to post some new content.

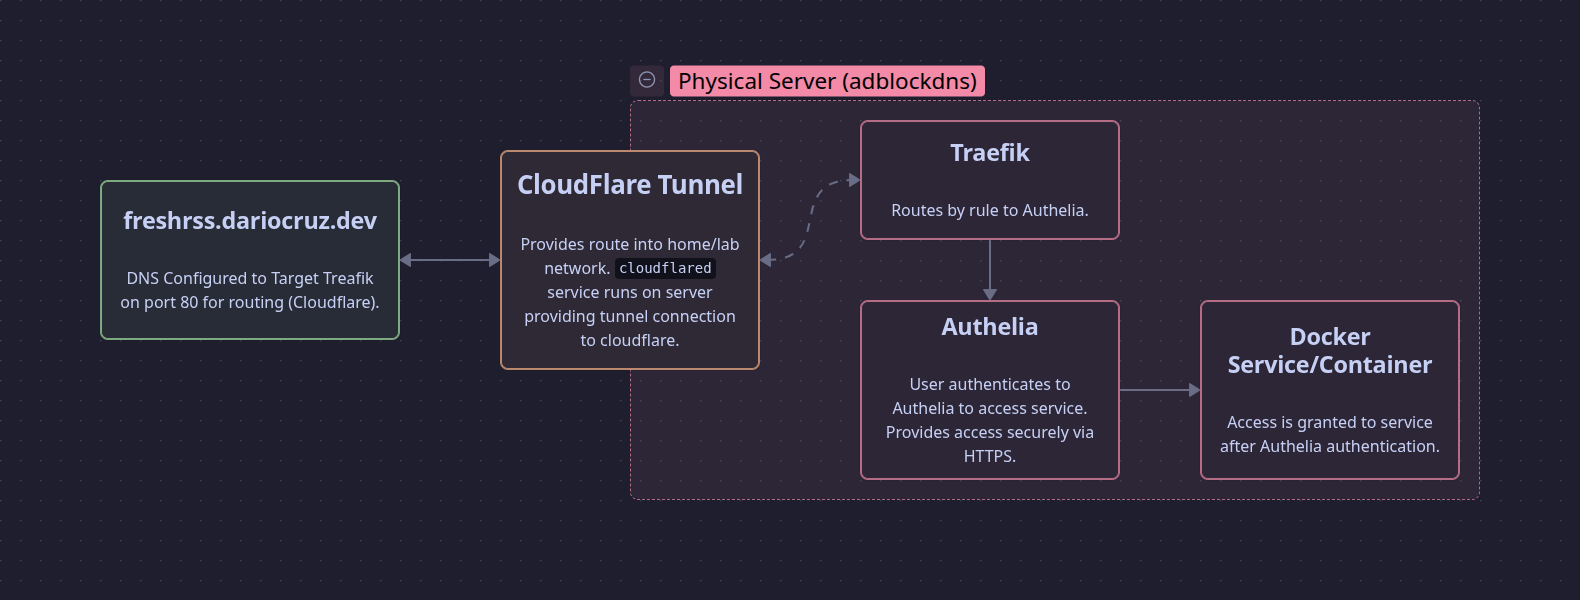
Recently, I have been working on building out a Docker server for some network services I wanted to implement, such as AdGuard and Unbound for local DNS resolution. This led me to investigate methods of exposing services running in my lab and home servers to the internet securely.

After researching various methods, I settled on implementing Cloudflare Tunnels alongside Traefik for the reverse proxy and Authelia for secure authentication.

Learning Linux with Arch

· 15 min read
Dario Cruz
Maintainer of DarioCruz.dev

Learning Linux with Arch - Title Image

Hello all,

I know that there has been some time between my previous post and this one. In recent months I have taken on a new role and have been ensuring that I have been taking on my role's responsibilities and tasks. This hasn't left much in the way of time for learning and exploring but, now that everything has settled down, I can dig into some new topics.

Unit42 (HTB-Sherlock)

· 12 min read
Dario Cruz
Maintainer of DarioCruz.dev

Title Image - Unit42

Welcome back everyone. The following Sherlock is being completed in preparation for taking the HTB CDSA exam. I came across a medium blog post by the user, Hammazahmed. He provides some advice for learning and practicing skills before taking the exam. Specifically, he mentioned this Sherlock investigation, along with some others, BFT, Noted, RogueOne (Which I have completed, full writeup here), and Meerkat.

Campfire 2 (HTB-Sherlock)

· 5 min read
Dario Cruz
Maintainer of DarioCruz.dev

Campfire2 - Main Title

On to the second part of the Campfire Sherlock from Hack the Box. Again, if you have not read my previous write-up on Campfire 1, go check it out. The aim is to complete all Sherlocks in the Detecting Active Directory Attacks track on HTB labs. Time to investigate!

The Scenario​

Forela's Network is constantly under attack. The security system raised an alert about an old admin account requesting a ticket from KDC on a domain controller. Inventory shows that this user account is not used as of now so you are tasked to take a look at this. This may be an AsREP roasting attack as anyone can request any user's ticket which has preauthentication disabled.